- Go to
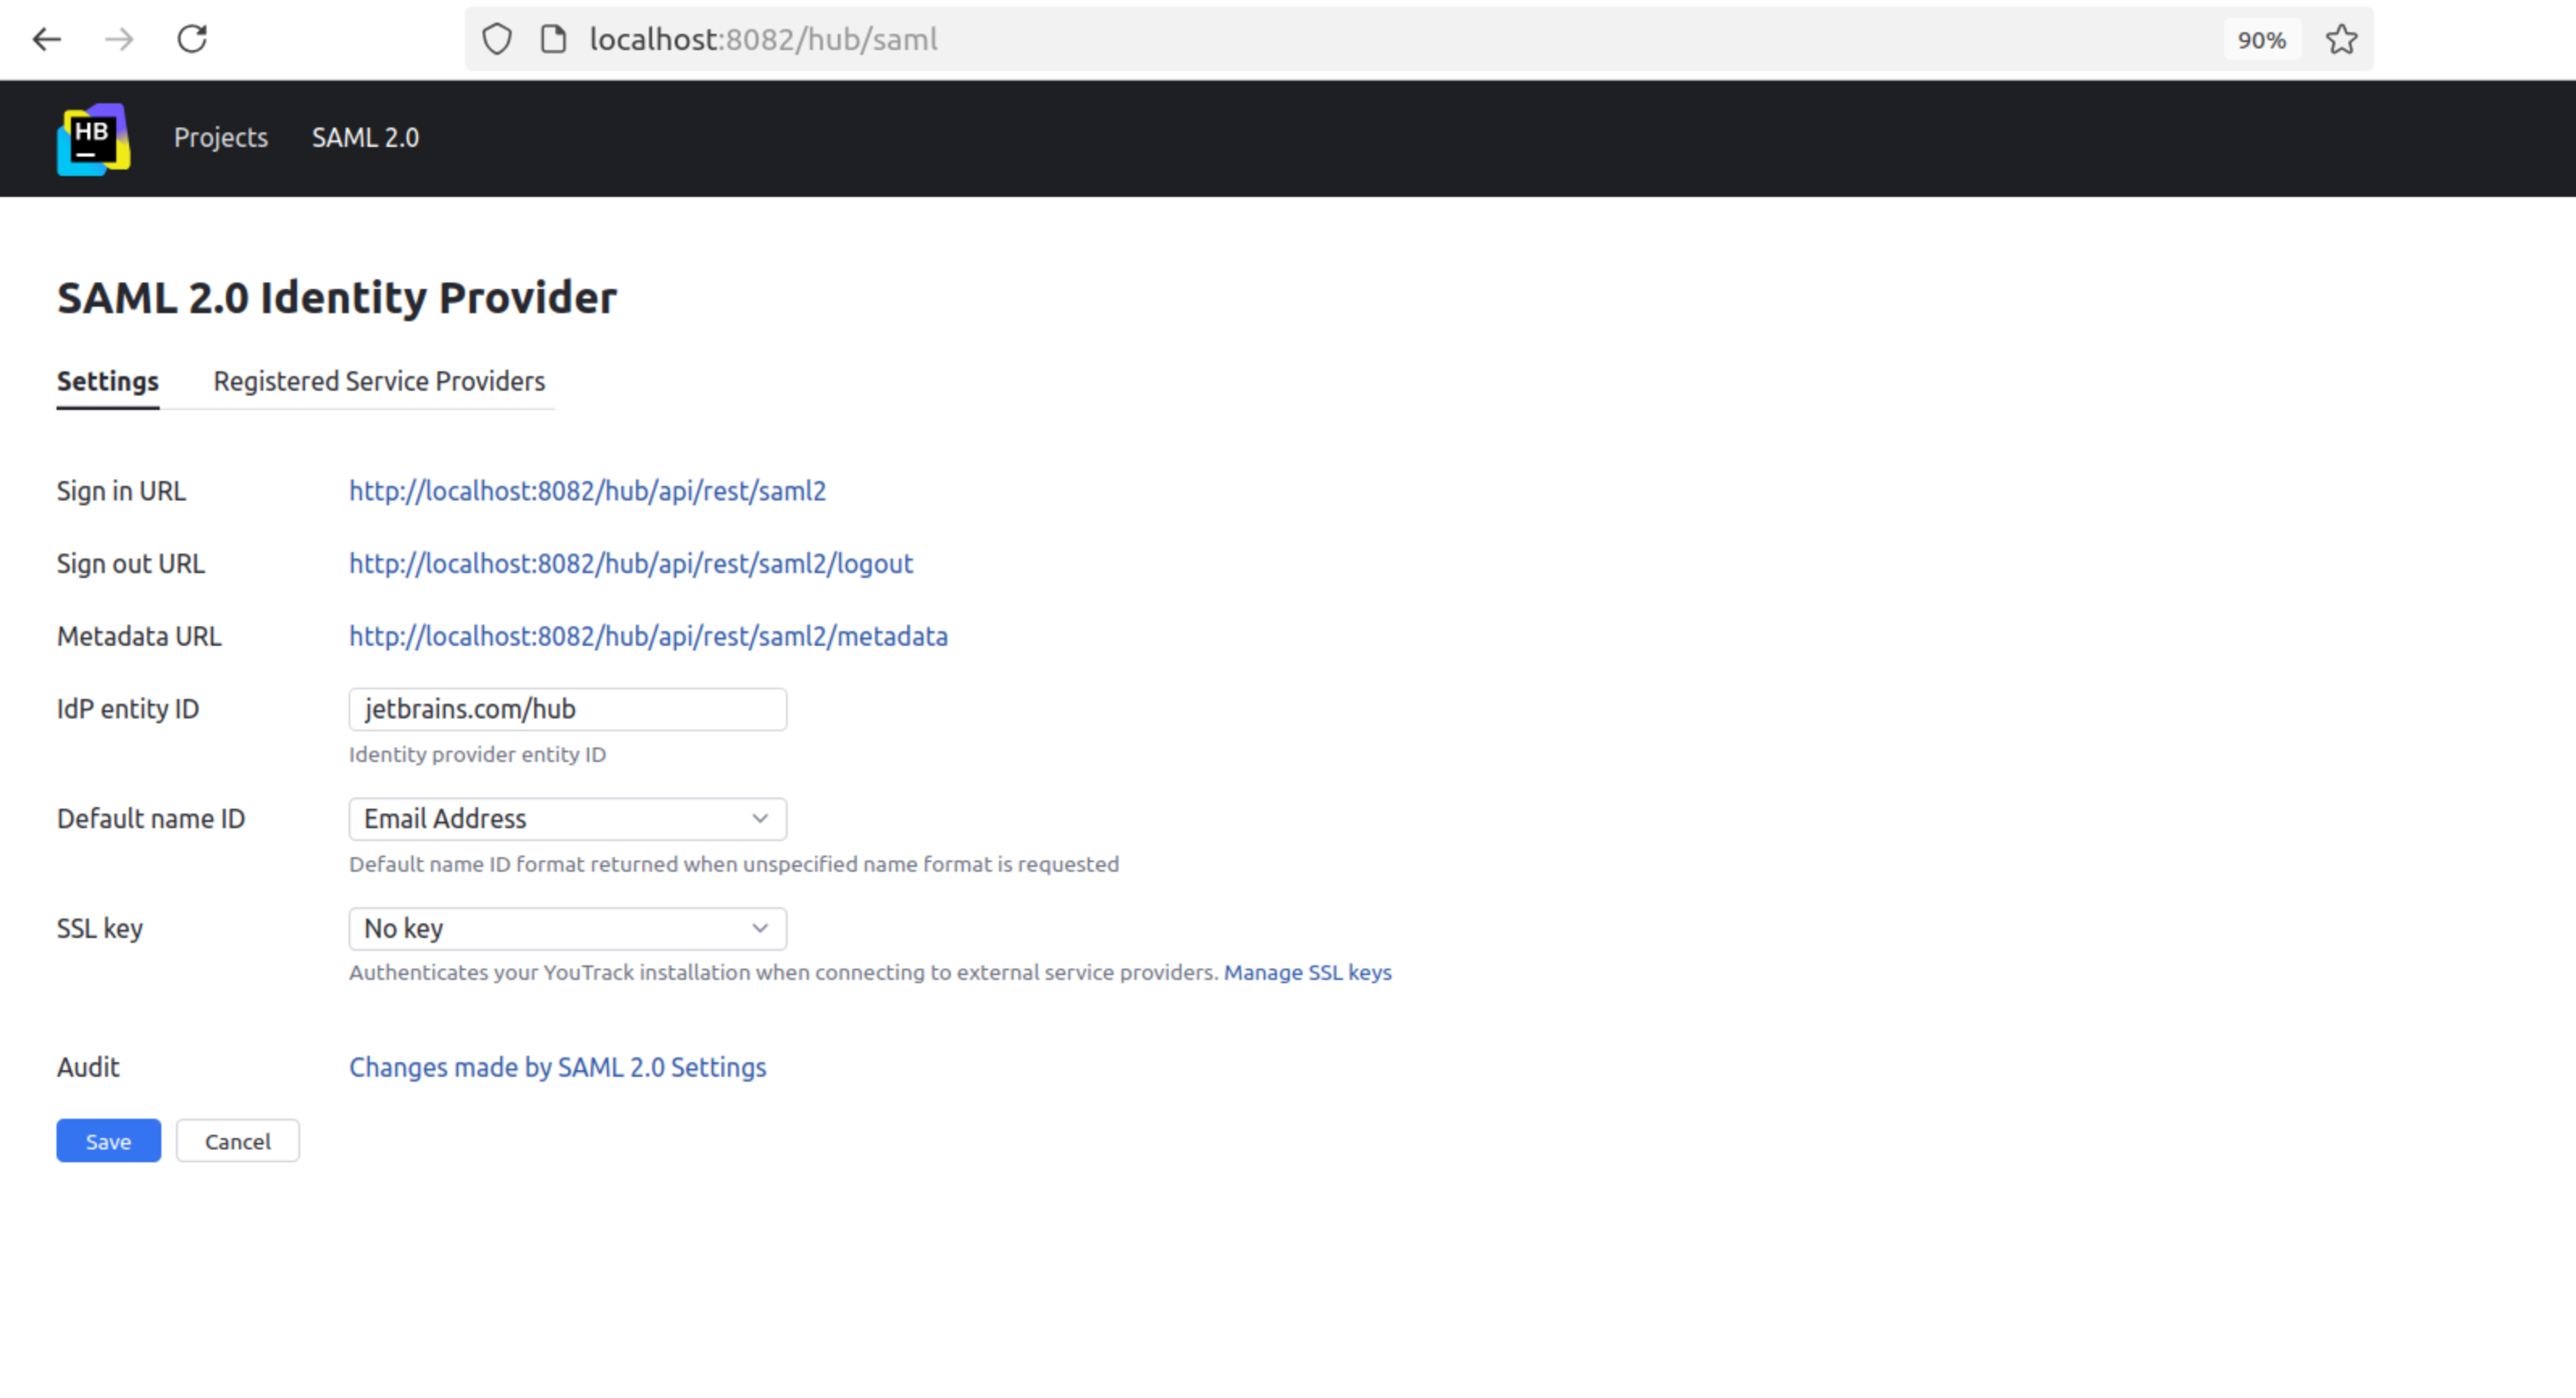
<hub-url>/hub/saml
- Write down URIs and IdP Identity ID
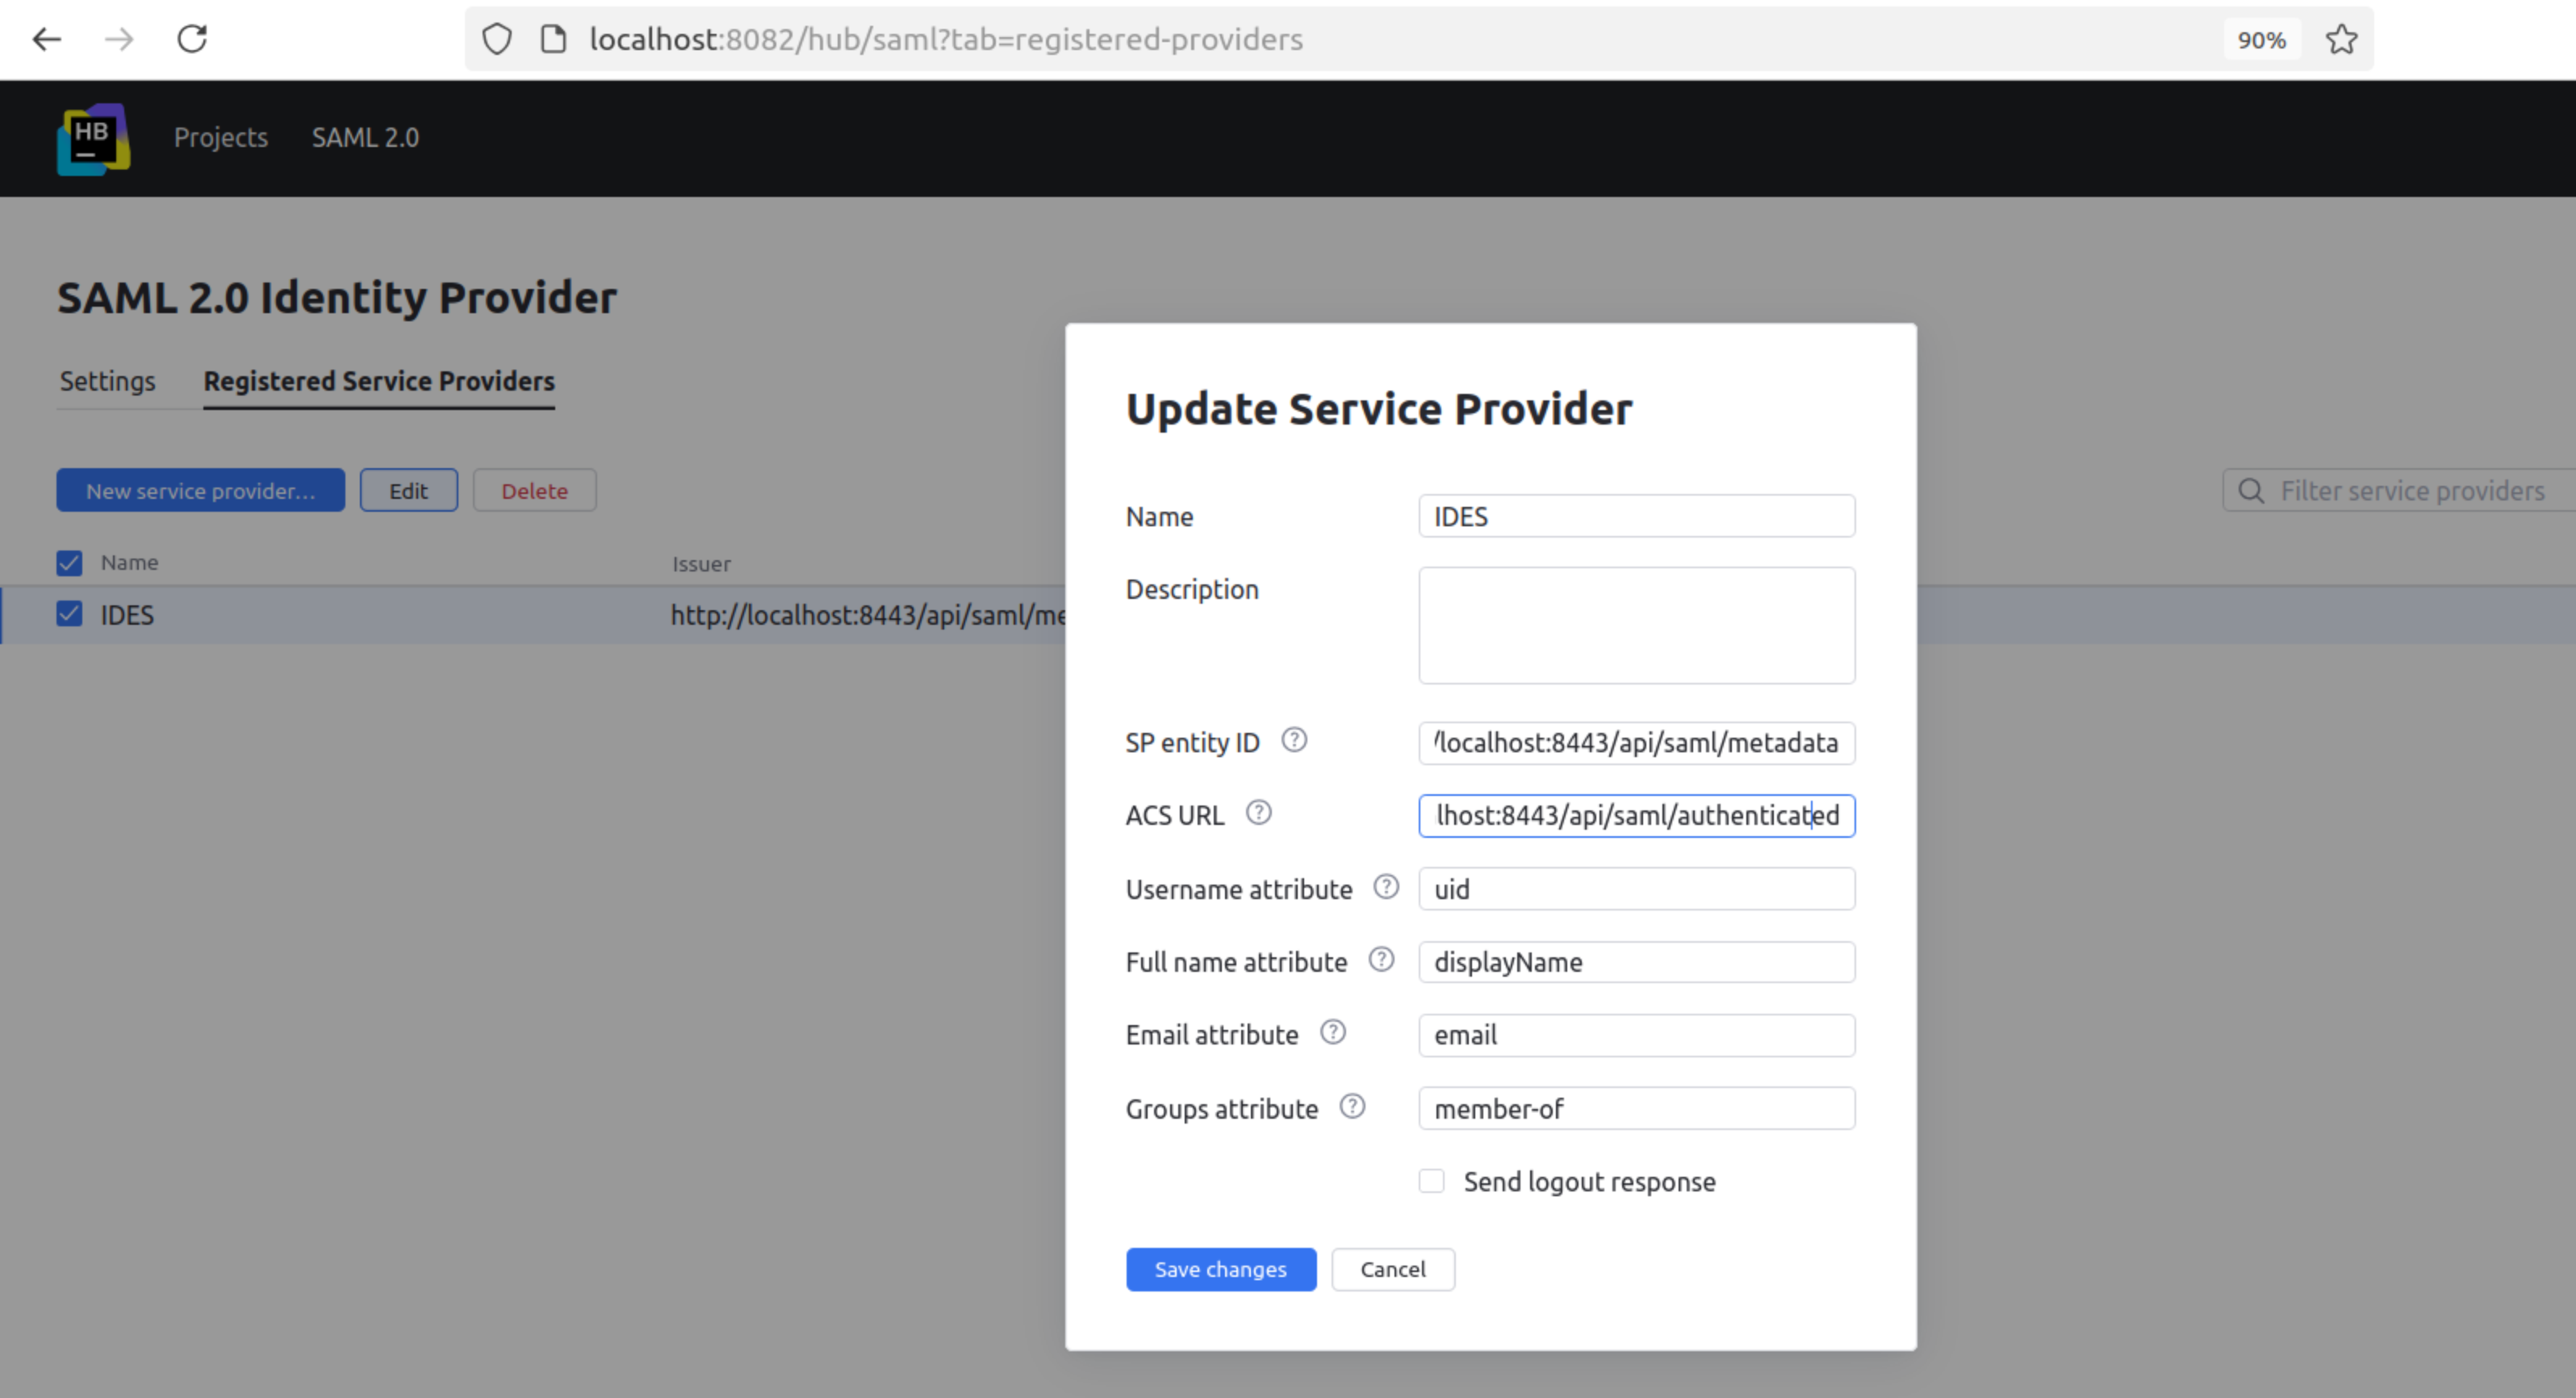
- Go to Registered Service Providers -> New service provider. Fill in fields accordingly:
- SP entity ID:
<ide-services-url>api/saml/metadata
- ACS URL:
<ide-services-url>/api/saml/authenticated
- Email attribute =
email (change from default mail)
- Save changes
- Prepare IDE Services certificates as per this guide: https://www.jetbrains.com/help/ide-services/saml.html#cert_key_generation
- Prepare Hub certificate and upload according to this guide: https://www.jetbrains.com/help/hub/set-up-ssl-keys-for-saml2-0.html
- upload Hub_SAML.p12 to to Hub as per guide
- save Hub_SAML.crt, we'll need it later
- Prepare application.yaml, see working example below for reference
- make sure to add
server.forward-headers-strategy: native
tbe.deployment.allowed-origins: "<hub_url>"-
http://localhost:8082 - URL of my Hub ( though https is preferred)
- notice certificates and their corresponding file names from step 4:
sp-x509cert: <local.crt> sp-private-key: <local.key>private-key: <private_key_pkcs8.pem> public-key: <public_key.pem>
- IDP certificate from step 5:
idp-x509cert: <Hub_SAML.crt>
server:
...
    forward-headers-strategy: native

tbe:
  deployment:
    url: 'http://localhost:8443'
    hsts:
      max-age-seconds: 0

    allowed-origins:
       - "hub_url"

  auth:
    internal-tokens:
      token-life: 30m
      refresh-token-life: 30d
      private-key: # https://www.jetbrains.com/help/ide-services/saml.html#-47k2sx_83
      public-key: # https://www.jetbrains.com/help/ide-services/saml.html#-47k2sx_84
    root-admin-emails:
      - "johndoe@example.com"
    saml:
        enabled: true
        sp-id: '${tbe.deployment.url}/api/saml/metadata'
        sp-assertion-consumer-service-url: '${tbe.deployment.url}/api/saml/authenticated'
        sp-x509cert: |-
          -----BEGIN CERTIFICATE-----
          ...
          -----END CERTIFICATE-----
        sp-private-key: |-
          -----BEGIN PRIVATE KEY-----
          ...
          -----END PRIVATE KEY-----
        sso-url: 'http://localhost:8082/hub/api/rest/saml2'
        idp-id: 'jetbrains.com/hub'
        idp-x509cert: |-
          -----BEGIN CERTIFICATE-----
          ...
          -----END CERTIFICATE-----
        cert-algorithm: sha256
        idp-http-method: 'POST' #optional
        attribute-mapping: #optional
            email: email
            firstName: first_name
            lastName: last_name
            fullName: full_name

Comments
0 comments
Please sign in to leave a comment.